AI Data Security: What Should You Never Share With an AI Tool?
Artificial intelligence is becoming part of everyday business operations. Employees use AI tools to draft emails, summarise documents, analyse spreadsheets, prepare reports and respond to customer enquiries. While these tools can improve productivity and reduce operating costs, they also introduce risks to confidential business information. AI Data Security is therefore an important consideration for businesses adopting these technologies. Understanding what information should never be shared with an AI tool, and how that information may be processed, stored or accessed, is essential to protecting customers, employees and the business itself.
However, the convenience of AI introduces an important question: what information is safe to share with an AI tool?
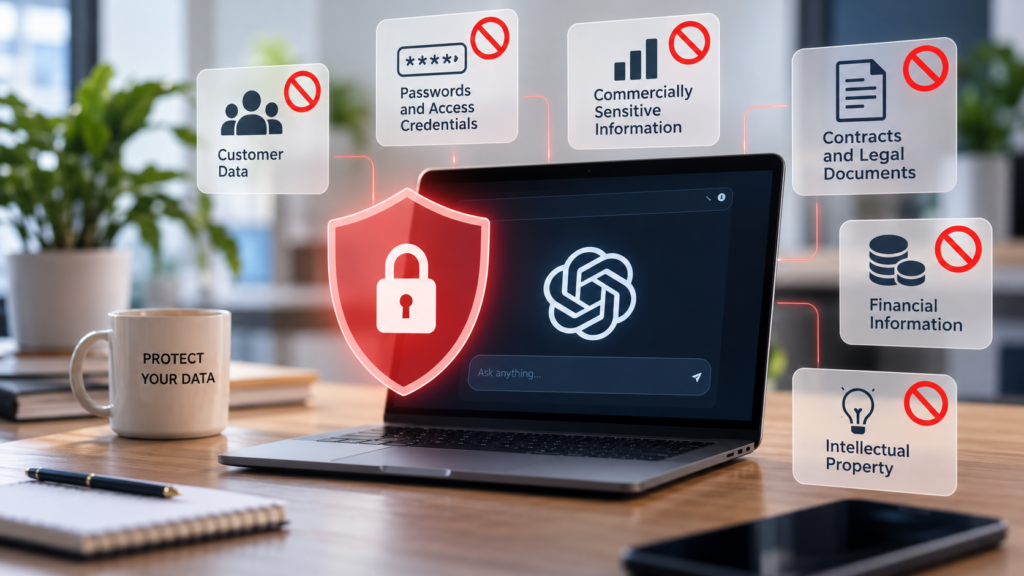
Consider a business owner who uploads a customer database into ChatGPT to identify sales opportunities. Another employee copies a confidential supplier agreement into an AI assistant and asks it to summarise the terms. A finance manager uploads a spreadsheet containing employee salaries, bank account details and company financial projections.
These activities may appear harmless. The employees are simply trying to complete their work more efficiently. Yet each action could expose information that the business has a legal, contractual or commercial obligation to protect.
The issue is not necessarily that AI tools are insecure. Many providers have implemented substantial security controls. The concern is that businesses may share information without understanding how it is processed, stored, retained or accessed.
This article examines the types of information businesses should avoid entering into AI tools, the risks involved and the controls needed to use AI responsibly.
1. Customer Personal Data
Customer information is one of the most important categories of data a business must protect.
Personal data includes any information relating to an identified or identifiable individual. This extends beyond names and email addresses to information that could identify someone when combined with other details.
Examples include:
- Customer names, addresses and telephone numbers.
- Email addresses and account identifiers.
- Dates of birth and identification documents.
- Purchase histories linked to identifiable customers.
- Customer complaints and correspondence.
- Medical information and other sensitive personal records.
Under the UK General Data Protection Regulation (UK GDPR), businesses must have a lawful basis for processing personal data and ensure that appropriate security measures are in place.
Using an AI tool to process customer information does not remove these responsibilities.
For example, a retailer may want to analyse customer purchasing patterns. Uploading a spreadsheet containing names, contact details and individual transaction histories into an unapproved AI service could create unnecessary privacy risks.
The business would need to understand whether the AI provider processes the information on its behalf, where the data is stored, whether it is transferred internationally and what contractual safeguards apply.
A safer approach
Where possible, remove personal identifiers before submitting information for analysis.
Instead of uploading individual customer records, provide aggregated information such as monthly sales by product category, average transaction values or customer retention percentages.
However, removing names alone does not guarantee anonymity. Individuals may still be identifiable through combinations of transaction dates, locations, unusual purchases or other characteristics.
If personal data must be processed through an AI service, the business should first establish that the tool is approved for that purpose and that the necessary privacy and security controls are in place.
2. Passwords, API Keys and Access Credentials
Passwords and access credentials should never be entered into general AI chat tools.
These credentials provide access to business systems, customer information, financial platforms and internal infrastructure.
Examples include:
- Employee and administrator passwords.
- Application programming interface (API) keys.
- Database connection credentials.
- Cloud service access tokens.
- Private encryption keys.
- Recovery codes and authentication secrets.
- Session tokens and other login credentials.
An employee troubleshooting a technical problem might copy an application configuration file into an AI assistant. That file could contain a database password or API key.
Similarly, a developer may paste a section of source code that includes a secret used to connect to a payment provider.
Once these credentials have been submitted, the business may no longer be able to establish confidently where copies exist or whether they have been retained.
Even where a provider states that customer content is not used for model training, that assurance does not mean submitted information is never stored or processed.
A safer approach
Replace credentials with clearly labelled placeholders before asking an AI tool for assistance.
For example, use DATABASE_PASSWORD rather than an actual password.
Businesses should also use dedicated secret management systems, restrict access to credentials and rotate secrets when exposure is suspected.
If a password or API key is accidentally submitted to an unauthorised AI service, treat it as potentially compromised. Revoke or rotate it promptly and investigate any associated access.
3. Commercially Sensitive Business Information
Not every important business record contains personal data.
Some information is commercially valuable because competitors, suppliers or other parties could benefit from obtaining it.
Examples include:
- Confidential pricing strategies.
- Customer acquisition plans.
- Supplier discounts and negotiated rates.
- Product launch schedules.
- Business expansion plans.
- Tender submissions and proposed bids.
- Acquisition discussions.
- Internal performance reports.
- Unannounced business decisions.
Consider a company preparing to submit a competitive tender.
An employee might upload the proposed pricing model, delivery strategy and internal cost assumptions into an AI tool to improve the presentation.
If the service has not been approved to process confidential business information, this may introduce a risk that the company has not assessed.
Commercial confidentiality also matters when businesses use AI tools that connect to external applications. A tool with broad access to shared drives, emails or project management systems may be able to retrieve more information than is necessary for a particular task.
A safer approach
Use fictional figures, generalised scenarios or publicly available information when seeking advice from AI.
For example, rather than providing a confidential supplier quotation, ask the tool to explain how to compare supplier pricing structures.
Where the actual information is necessary, use an approved business AI environment with appropriate access controls, contractual protections and retention settings.
4. Confidential Contracts and Legal Documents
Contracts frequently contain information that should not be disclosed outside the parties involved.
These documents may include commercial terms, personal information, financial commitments, intellectual property provisions and confidentiality obligations.
Examples include:
- Employment agreements.
- Supplier and customer contracts.
- Nondisclosure agreements.
- Shareholder agreements.
- Settlement agreements.
- Commercial leases.
- Merger and acquisition documents.
- Confidential legal advice.
A business owner may upload a supplier agreement into an AI tool to identify termination clauses or payment obligations.
Although this may save time, the agreement could contain information protected by contractual confidentiality provisions.
There may also be concerns about legal professional privilege where confidential communications involving legal advisers are shared with third parties.
Whether privilege or confidentiality is affected depends on the circumstances, including the nature of the information, the service and the applicable legal rules. It should not be assumed that using an AI tool automatically preserves these protections.
A safer approach
For general questions, provide a description of the contractual issue without including names, negotiated figures or confidential clauses.
If an actual contract requires AI analysis, confirm that the service is authorised for confidential legal documents and that appropriate contractual and security safeguards apply.
AI can assist with identifying clauses and explaining terminology, but important legal conclusions should still be reviewed by a suitably qualified professional.
5. Financial Information and Banking Details
Financial information is particularly sensitive because unauthorised disclosure can lead to fraud, financial loss and commercial damage.
Businesses regularly handle information such as:
- Bank account numbers and payment details.
- Credit and debit card information.
- Payroll records and employee salaries.
- Customer invoices and payment histories.
- Tax records and supporting schedules.
- Management accounts.
- Cash flow forecasts.
- Profit margins and financial projections.
- Investment and financing arrangements.
An accountant or finance manager might upload a full bank statement to an AI tool and request a cash flow analysis.
The document may contain account numbers, customer references, supplier names, payment descriptions and other confidential details.
The risk extends beyond the possibility of a data breach. Financial records can reveal business relationships, spending patterns and commercially sensitive activities.
There may also be specific obligations under payment card security standards, professional confidentiality requirements and contractual agreements.
A safer approach
Use aggregated or appropriately redacted financial information for general analysis.
For example, a business seeking help with cash flow forecasting could provide monthly totals for sales, operating expenses, loan repayments and cash balances without disclosing account numbers or transaction counterparties.
Where detailed financial records are essential, use a properly assessed service authorised to process that category of information.
For businesses subject to the Payment Card Industry Data Security Standard, payment card data must be handled in accordance with the applicable requirements. Sensitive authentication data, such as card verification codes, should not be submitted to general AI tools.
6. Intellectual Property and Unreleased Business Ideas
Intellectual property is often one of a business’s most valuable assets.
It may include software source code, proprietary algorithms, product designs, manufacturing methods, research findings and confidential technical documentation.
Examples include:
- Unreleased product designs.
- Proprietary source code.
- Internal software architecture.
- Research and development findings.
- Patentable inventions.
- Trade secrets.
- Confidential product specifications.
- Original creative materials.
- Unpublished marketing concepts.
Consider a software company developing a new product.
A developer may upload substantial sections of proprietary source code to an AI coding assistant for debugging or optimisation.
Whether this is acceptable depends on the company’s policies, contractual obligations and the AI service’s data handling arrangements.
It is also important to distinguish between copyright ownership, confidentiality and trade secret protection.
Submitting information to an AI service does not automatically transfer ownership of intellectual property to the provider. However, inappropriate disclosure could create confidentiality risks and, in some circumstances, affect the protection available for trade secrets or inventions.
A safer approach
Businesses should establish clear rules governing the use of AI coding assistants and other tools that process intellectual property.
Approved services should have suitable contractual terms, access restrictions and data retention arrangements.
Where possible, submit only the relevant section of code or a simplified example rather than an entire proprietary codebase.
For inventions or confidential research, seek appropriate professional advice before disclosing material to an external service.
7. Employee Information and Internal HR Records
Businesses must also protect information relating to their employees.
Human resources records often contain sensitive personal information and confidential assessments.
Examples include:
- Employee salaries and benefits.
- Performance reviews.
- Disciplinary records.
- Recruitment assessments.
- Absence and sickness records.
- Medical information.
- Grievance complaints.
- Redundancy proposals.
- Background checks.
An HR manager might use AI to draft a performance review or summarise an employee grievance.
If the manager copies the employee’s complete record into an unapproved AI tool, the business may create privacy and confidentiality risks.
Information concerning health, ethnicity, religious beliefs and certain other characteristics may qualify as special category personal data under UK GDPR, requiring additional safeguards.
A safer approach
Use anonymised examples when asking AI to help prepare HR templates, policies or general communications.
Where AI is used to support actual employment decisions, businesses should assess the lawful basis, fairness, accuracy and transparency of the processing.
AI generated recommendations should not be accepted without appropriate human review, particularly where they could materially affect an employee.
8. Internal Security Information and System Configurations
Some information may appear technical rather than confidential, but disclosing it could make a business more vulnerable to cyberattacks.
Examples include:
- Network diagrams.
- Firewall configurations.
- Internal IP addresses and system inventories.
- Security vulnerability reports.
- Penetration testing findings.
- Administrative access procedures.
- Backup and recovery arrangements.
- Details of unresolved security weaknesses.
A system administrator might upload an internal security assessment and ask an AI tool to recommend improvements.
Although the intention is to strengthen security, the document may reveal weaknesses that have not yet been corrected.
A safer approach
Use approved security tools and controlled AI environments for analysing sensitive infrastructure information.
Remove unnecessary system identifiers and access details from general enquiries.
Security teams should also review the permissions granted to AI agents that can access repositories, cloud infrastructure, databases or internal documents.
An AI agent capable of performing actions presents additional risks because it may not simply read information. Depending on its permissions, it may also modify files, execute commands or transmit data to external services.
Does This Mean Businesses Should Never Use AI With Confidential Data?
No.
The important distinction is between using an AI service that has been properly assessed and approved for a specific purpose, and submitting sensitive information to an unapproved tool.
Some business AI services provide contractual commitments covering data processing, retention, security and the use of submitted information for model training.
However, these arrangements differ between providers, products, subscription plans and configurations.
A paid subscription alone does not establish that a service is suitable for processing confidential information.
Before approving an AI tool, businesses should understand:
- Data processing: What information does the provider collect and how is it used?
- Data retention: How long is submitted information stored and can it be deleted?
- Model training: Is business information used to train or improve AI models?
- Access controls: Who can access submitted information and connected systems?
- Data location: Where is information processed and what international transfers may occur?
- Contractual safeguards: Are appropriate data processing and confidentiality agreements available?
- Security measures: What protections exist for encryption, authentication, monitoring and incident response?
- Third parties: Are other providers or subprocessors involved in handling the information?
Businesses should also consider whether an AI tool needs access to the information at all.
The principle of data minimisation remains relevant: provide only the information necessary to achieve the intended purpose.
A Practical Information Classification Framework for AI Use
Businesses do not need an elaborate governance department to establish basic information handling rules.
A simple classification framework can help employees understand what they may share with AI tools.
| Information category | Examples | Recommended AI use |
|---|---|---|
| Public | Published website content, public reports, general product information | Generally suitable for approved AI tools |
| Internal | Routine procedures, general internal templates | Permitted where company policy allows |
| Confidential | Customer records, contracts, financial reports, pricing strategies | Only through specifically approved services with suitable controls |
| Restricted | Passwords, private keys, authentication secrets, highly sensitive security information | Do not enter into general AI tools; use dedicated authorised systems |
This framework should form part of the company’s internal AI policy.
Employees should understand that permission to use an AI tool does not automatically mean permission to upload every category of business information.
What Should You Do If Sensitive Information Has Already Been Shared?
Accidental disclosure can occur even where policies and training are in place.
A business should respond promptly rather than assuming that deleting a conversation resolves the issue.
The following actions provide a practical starting point.
1. Identify what was shared. Establish the information involved, the AI service used, the account concerned and when the disclosure occurred.
2. Contain the exposure. Where appropriate, restrict access, revoke credentials and disable affected integrations. Use available deletion controls, while recognising that deletion from the interface may not remove every retained copy.
3. Assess the risk. Determine whether personal data, confidential commercial information or security credentials were involved. Review the provider’s relevant data handling terms.
4. Record the incident. Maintain a factual record of what happened, the potential consequences and the actions taken.
5. Consider notification obligations. Under UK GDPR, certain personal data breaches must be reported to the Information Commissioner’s Office within 72 hours of becoming aware of the breach, where feasible. Not every incident is reportable. The obligation depends on the risk to individuals, and notification to affected individuals may also be required where the risk is high.
6. Improve existing controls. Review staff guidance, approved tools, access permissions and training to reduce the likelihood of a similar incident.
Businesses should avoid assuming that every accidental AI submission constitutes a reportable personal data breach. The facts and the applicable legal requirements must be assessed.
How Small Businesses Can Reduce AI Data Security Risks
A practical AI security programme should focus on a manageable number of controls that employees can follow consistently.
Create an approved AI tools register
Identify which tools employees may use and the types of information each service is authorised to process.
Introduce clear information classification rules
Explain which information is public, internal, confidential or restricted.
Train employees using realistic examples
Demonstrate how to remove personal identifiers, confidential figures and credentials before submitting information.
Control integrations and agent permissions
Restrict access to shared drives, email systems, databases and business applications according to the tasks employees need to perform.
Review AI use regularly
Reassess tools when providers change their terms, new features are introduced or the business begins processing different types of information.
These measures should be proportionate to the size of the business, the information it handles and the risks associated with its activities.
AI Security Is a Business Responsibility
AI tools can help businesses work more efficiently, but they do not remove existing responsibilities for information security, privacy and confidentiality.
A business remains responsible for deciding what information employees may disclose, which services are appropriate and what controls must be applied.
The objective is not to prevent employees from using AI. It is to ensure that AI adoption does not introduce avoidable risks to customers, employees, business partners or the organisation itself.
Before entering information into an AI tool, employees should ask three questions:
Does the tool need this information? Am I authorised to share it? Has the business approved this tool to handle it?
If the answer to any of these questions is unclear, the information should not be submitted until the position has been confirmed.
A few seconds spent checking what is being shared can prevent a much more serious security incident.
Building on Your Business AI Policy
This article forms part of Tookand’s series on AI adoption, governance and security for small businesses.
In our previous article, Your Business Needs an AI Policy — Even If You Only Use ChatGPT, we examined why organisations need clear rules covering approved AI tools, data handling, human review and accountability.
The next step is putting those rules into everyday practice. Understanding which information should never be shared with an unapproved AI tool is an essential part of protecting the business while benefiting from the technology.
At Tookand, we believe that responsible technology adoption starts with clear business objectives, proportionate controls and practical governance. Businesses that establish these foundations will be better positioned to use AI productively without compromising the information entrusted to them.
References and Further Reading
The following official resources provide further guidance on data protection, AI security and information governance.
1. Information Commissioner’s Office (ICO): Artificial intelligence and data protection — Guidance on applying data protection requirements to AI systems.
2. ICO: Personal data breaches — Guidance on assessing and reporting personal data breaches.
3. National Cyber Security Centre (NCSC): Guidelines for secure AI system development — Security principles covering AI system development, deployment and operation.
4. UK Government: UK General Data Protection Regulation — The legal framework governing the processing of personal data in the United Kingdom.
5. NCSC: Cyber security guidance for small businesses — Practical measures to protect business systems and information.